RSS
Showing posts with label Hacking Tutorials. Show all posts

Ultimate® Wireless Hacking Guide For Beginners With Commview For WiFi


CommView®
CommView is a powerful network monitor and analyzer designed for LAN administrators, security professionals, network programmers, home users…virtually anyone who wants a full picture of the traffic flowing through a PC or LAN segment. Loaded with many user-friendly features, CommView combines performance and flexibility with an ease of use unmatched in the industry. In this thread I will provide you with software download and Manual on how to do it all by yourself! This is the one and only most noob proof guide ever made! You will be able to hack any W-LAN in your range with ease and safety. The software provided is cracked and not infected anyhow.
This application captures every packet on the wire to display important information such as a list of packets and network connections, vital statistics, protocol distribution charts, and so on. You can examine, save, filter, import and export captured packets, view protocol decodes down to the lowest layer with full analysis of over 70 widespread protocols. With this information, CommView can help you pinpoint network problems and troubleshoot software and hardware.
How can a network analyzer help me?
If you are a seasoned professional, you definitely know the answer. Managing a LAN, creating network-oriented software, or performing a security audit have one thing in common: You’re blind without a good network monitor. Every day, it helps you maintain efficient network data transmission, test firewalls and intrusion detection systems, or identify problems with network-based applications. And there is an important economic reason behind using a network analyzer: it costs a fraction of the price of information, time, software, and hardware that may potentially be lost or wasted by not using a network analyzer. A number of case studies describe real-world applications of CommView in business, government, and education sectors.
If you are new to networking, you’ll find CommView extremely useful for understanding how the Internet and your LAN work. Being a network analyzer (also commonly referred to as a packet analyzer, network monitor, or packet sniffer), it captures and decodes network traffic and makes sense of it, allowing you to see what, where, and how information leaves and enters your computer — which is critically important for a secure Internet experience. The Online Tutorial is an excellent resource for learning about the many exciting features CommView offers.

What you can do with CommView:

* View detailed IP connections statistics: IP addresses, ports, sessions, etc.
* Reconstruct TCP sessions.
* Map packets to the application that is sending or receiving them.
* View protocols distribution, bandwidth utilization, and network nodes charts and tables.
* Generate traffic reports in real time.
* Browse captured and decoded packets in real time.
* Search for strings or hex data in captured packet contents.
* Import and export packets in Sniffer®, EtherPeek™, AiroPeek™, Observer®, NetMon, and Tcpdump formats, export packets in hex and text formats.
* Configure alarms that can notify you about important events, such as suspicious packets, high bandwidth utilization, unknown addresses, etc.
* Create your own plug-ins for decoding any protocol.
* Exchange data with your application over TCP/IP.
* Export any IP address to SmartWhois for quick, easy IP lookup.
* Capture loopback traffic (a new, unique feature in version 4.1).
Commview Download:
http://www.mediafire.com/?j2vntwidnmk <—Install it and crack it as any other application.
Wireless Hacking Plug in + Manual Download:
http://www.mediafire.com/?j2uuymzw3mt <— Run the application and read the manual to help you with process

read comments Read User's Comments

RAT(Remote Administration Tool) Guide For Beginners- Q&A. Explained


Remote Administrator Tools Q & A.

Q – Whats RAT?
A – A RAT is also a shortcut called Remote Administrator Tool. It is mostly used for malicious purposes, such as controlling PC’s, stealing victims data, deleting or editing some files. You can only infect someone by sending him file called Server and they need to click it.
Q – How they work?
A - Some RATs can spread over P2P file sharing programs(uTorrent, Pirate Bay etc.), Messangers spams(MSN, Skype, AIM etc.).
Q – Download?
A – Well you can find any type of RAT here, on beginnershacking.wordpress.com. To download.  and you will find some links. Also, you can buy FUD private version of RAT: Albertino RAT, Medusa Rat, jRAT etc. Also you will need DNS host for your RAT.
Q – How do I control server?
A - Once installed, RAT server can be controlled via RAT client. From IP list box you choose PC and connect.
Q – What do I need to setup RAT?
A - Well, you will need Windows OS, open port & RAT. To forward your port scroll for tutorial link or click this URL.

Q – How do I port forward?

A – Port forwarding is easy and important for RAT. Well, you need open port because RAT connects through open port and bypass firewall. Open your web browser and write your IP and connect to your rooter(write Username: Admin & Password: Admin), open port forward page and write port you want and your IP. Well that’s all you need to do and now you got open port

Q – How do I make my server FUD?

A - If you want to make your server FUD again, you will need crypter(you can find free FUD one here.). Also, you can hex edit your server, but be careful some servers can crash after hex editing, any way check out this cool tutorial How to make FUD with hex editing.
Q – How do I remove server if I infect myself?
A - When you infect yourself, first what you going to do is to connect to your PC. Some RATs have function to uninstall servers, well you click that and you uninstall it. Well there is another way, download MalwareBytes’ Anti-Malware and scan whole computer for Trojan.
Q – Legal or illegal?
A - Well some RATs are legal, and some are not. Legal are the one without backdoor left, and they have abillity to close connection anytime. Illegal are used for hacking and they can steal data(Credit Cards, Passwords, private data etc.).
Legal:
  • TeamViewer – Access any remote computer via Internet just like sitting in front of it – even through firewalls.
  • UltraVNC – Remote support software for on demand remote computer support. VNC.Specializing in Remote Computer Support, goto my pc, goto assist, Remote Maintenance
  • Ammyy Admin – Ammyy Admin is a highly reliable and very friendly tool for remote computer access. You can provide remote assistance, remote administration or remote
  • Mikogo – Mikogo is an Online Meeting, Web Conferencing & Remote Support tool where you can share your screen with 10 participants in real-time over the Web.
Illegal:
  • Spy-Net
  • Cerberus Rat
  • CyberGate Rat
  • SubSeven
  • Turkojan
  • ProRat
To Download This RAT’s  Click Here
Q – Where and how do I spread?
A – There are few different ways to spread your server. You can spread on warez websites, P2P file sharing websites(uTorrent, Pirate bay etc.), YouTube etc. Well some people use custom made Auto-Spreaders programs to spread their server. But best and most effective way to spread is when you FUD your server.

Q – Whats DNS host?

A - The Domain Name System (DNS) is a hierarchical naming system for computers, services, or any resource connected to the Internet or a private network. It associates various information with domain names assigned to each of the participants. Most importantly, it translates domain names meaningful to humans into the numerical (binary) identifiers associated with networking equipment for the purpose of locating and addressing these devices worldwide.
Q – What can RAT do?
A – Here is list of basic features:
    • Manage files • Control web browser(Change homepage, open site etc.) • Get system informations(OS Version, AV name, Ram Memory, Computer name etc.) • Get passwords, credit card numbers or private data etc. • View and remote control desktop • Record camera & sound • Control mouse • Delete, rename, download, upload or move files
Q – What’s reverse Connection?
A - A reverse connection is usually used to bypass firewall restrictions on open ports. The most common way a reverse connection is used is to bypass firewall and Router security restrictions.
Q – Whats direct connection?
A - A direct-connect RAT is a simple setup where the client connects to a single or multiple servers directly. Stable servers are multi-threaded, allowing for multiple clients to be connected, along with increased reliability.
Q – Can I get traced when I rat somebody?
A – Yes and no. Depends on victim, it is really hard to remove infection or even trace a hacker. There are tools like WireShark, but it’s really hard to trace, because PC usually got over 300 connections. So don’t worry.
Direct connection:
Code:
[Client]
|    [Client]
|      /
|     /
|    /
|   /
[Server]-----[Client]

read comments Read User's Comments

Certified Ethical Hacker v6 Training Complete + All Laps DVD Download

Certified Ethical Hacker v6 Training

If you want to stop hackers from invading your network, first you’ve got to invade their minds.
Computers around the world are systematically being victimized by rampant hacking. This hacking is not only widespread, but is being executed so flawlessly that the attackers compromise a system, steal everything of value and completely erase their tracks within 20 minutes.
The goal of the ethical hacker is to help the organization take preemptive measures against malicious attacks by attacking the system himself; all the while staying within legal limits. This philosophy stems from the proven practice of trying to catch a thief, by thinking like a thief. As technology advances and organization depend on technology increasingly, information assets have evolved into critical components of survival.
If hacking involves creativity and thinking ‘out-of-the-box’, then vulnerability testing and security audits will not ensure the security proofing of an organization. To ensure that organizations have adequately protected their information assets, they must adopt the approach of ‘defense in depth’. In other words, they must penetrate their networks and assess the security posture for vulnerabilities and exposure.
The definition of an Ethical Hacker is very similar to a Penetration Tester. The Ethical Hacker is an individual who is usually employed with the organization and who can be trusted to undertake an attempt to penetrate networks and/or computer systems using the same methods as a Hacker. Hacking is a felony in the United States and most other countries. When it is done by request and under a contract between an Ethical Hacker and an organization, it is legal. The most important point is that an Ethical Hacker has authorization to probe the target.
The CEH Program certifies individuals in the specific network security discipline of Ethical Hacking from a vendor-neutral perspective. The Certified Ethical Hacker certification will fortify the application knowledge of security officers, auditors, security professionals, site administrators, and anyone who is concerned about the integrity of the network infrastructure. A Certified Ethical Hacker is a skilled professional who understands and knows how to look for the weaknesses and vulnerabilities in target systems and uses the same knowledge and tools as a malicious hacker.
To achieve the Certified Ethical Hacker Certification, you must pass the CEH exam 312-50

MEGAUPLOAD

DVD 1
http://www.megaupload.com/?d=WJMA05ZV
http://www.megaupload.com/?d=8C4MXDU5
http://www.megaupload.com/?d=JEVIK8N9
http://www.megaupload.com/?d=U6GD1WLL
http://www.megaupload.com/?d=E236PHW5
http://www.megaupload.com/?d=FQS8D87U
http://www.megaupload.com/?d=48STXW0A
http://www.megaupload.com/?d=G0SGLZ78
http://www.megaupload.com/?d=1J9SJ6FP
http://www.megaupload.com/?d=LMLUDROY
http://www.megaupload.com/?d=LJPF2LIY
http://www.megaupload.com/?d=45XI28TH
http://www.megaupload.com/?d=YN22OTE5
http://www.megaupload.com/?d=CONWEP1T
http://www.megaupload.com/?d=XZ49PRDZ
http://www.megaupload.com/?d=V7LNVLXR
http://www.megaupload.com/?d=ESYMRBKD
http://www.megaupload.com/?d=MYE7M5X2
http://www.megaupload.com/?d=LQ2E4L3F
http://www.megaupload.com/?d=83PYQ2FJ
http://www.megaupload.com/?d=BY7F9D9E
http://www.megaupload.com/?d=0F7CB4SW
http://www.megaupload.com/?d=SECJTNV8
http://www.megaupload.com/?d=4NIVW0K6
http://www.megaupload.com/?d=2TZTW8XM
http://www.megaupload.com/?d=BQT27X37
http://www.megaupload.com/?d=5NRZYDOW
http://www.megaupload.com/?d=VCR1NM0L
http://www.megaupload.com/?d=NLJ5E4IK
http://www.megaupload.com/?d=X43PWTRF
http://www.megaupload.com/?d=99GYQQWO
http://www.megaupload.com/?d=FZ0IJTHB
http://www.megaupload.com/?d=FPRXP0WT
http://www.megaupload.com/?d=78HQQ3PP
http://www.megaupload.com/?d=0MIU2MBN
http://www.megaupload.com/?d=U1NVSP4O
http://www.megaupload.com/?d=GY9K3319
http://www.megaupload.com/?d=RS5KUOEC
http://www.megaupload.com/?d=QQSKWY52
http://www.megaupload.com/?d=54VEQL5R
http://www.megaupload.com/?d=774K7H76

DVD 2
http://www.megaupload.com/?d=MLT21C3U
http://www.megaupload.com/?d=42KY3SXB
http://www.megaupload.com/?d=IC87L0IP
http://www.megaupload.com/?d=FY4UWBMC
http://www.megaupload.com/?d=IPNZTWWO
http://www.megaupload.com/?d=GO84L25S
http://www.megaupload.com/?d=QHBOCEP1
http://www.megaupload.com/?d=F403CEKN
http://www.megaupload.com/?d=M4HEUNWS
http://www.megaupload.com/?d=0FYJZ3RL
http://www.megaupload.com/?d=F85VS7AZ
http://www.megaupload.com/?d=BHZBJIX4
http://www.megaupload.com/?d=06ROVFYN
http://www.megaupload.com/?d=TB98UCR8
http://www.megaupload.com/?d=OHUEA7JZ
http://www.megaupload.com/?d=E45F9CE1
http://www.megaupload.com/?d=DYJXVMF6
http://www.megaupload.com/?d=IT3DWGQ9
http://www.megaupload.com/?d=4HL29MNO
http://www.megaupload.com/?d=XADBA8ZI
http://www.megaupload.com/?d=HEO81CJL
http://www.megaupload.com/?d=YV29FF5E
http://www.megaupload.com/?d=FTS7KWJI
http://www.megaupload.com/?d=MX7LFSHS
http://www.megaupload.com/?d=Z38Y8ONB
http://www.megaupload.com/?d=S868JPA0
http://www.megaupload.com/?d=W8FXON8A
http://www.megaupload.com/?d=A7CGNQBM
http://www.megaupload.com/?d=SB3ZE0YJ
http://www.megaupload.com/?d=48NJ0MU1
http://www.megaupload.com/?d=7WMOSEFG
http://www.megaupload.com/?d=WS10XE1M
http://www.megaupload.com/?d=ZIRPZ4US
http://www.megaupload.com/?d=O8GD4G4V
http://www.megaupload.com/?d=0CRQ3LUX
http://www.megaupload.com/?d=7GHB60H0
http://www.megaupload.com/?d=E9TV2AAC

DVD 3
http://www.megaupload.com/?d=OVCVUUKL
http://www.megaupload.com/?d=F25F9LSN
http://www.megaupload.com/?d=I871A71D
http://www.megaupload.com/?d=P23JGZII
http://www.megaupload.com/?d=CPOAGXTS
http://www.megaupload.com/?d=XOK19RWZ
http://www.megaupload.com/?d=NDBNUVQF
http://www.megaupload.com/?d=OKX9S9RW
http://www.megaupload.com/?d=RJC22B24
http://www.megaupload.com/?d=6HW73R6W
http://www.megaupload.com/?d=BYMZ5TPT
http://www.megaupload.com/?d=ZUYUTWGR
http://www.megaupload.com/?d=LUZK0AAI
http://www.megaupload.com/?d=ARZDBQYZ
http://www.megaupload.com/?d=Y3Z6YHBJ
http://www.megaupload.com/?d=UQ84L9JP
http://www.megaupload.com/?d=5ROOUKCA
http://www.megaupload.com/?d=I7L6GDO4
http://www.megaupload.com/?d=PC4MX7BP
http://www.megaupload.com/?d=KSBCN677
http://www.megaupload.com/?d=DGZF5OGI
http://www.megaupload.com/?d=TQVJY8R1
http://www.megaupload.com/?d=Q3I0U93I
http://www.megaupload.com/?d=G31NGGC0
http://www.megaupload.com/?d=1U3P0FP4
http://www.megaupload.com/?d=7A6QMJU4
http://www.megaupload.com/?d=5R22Z1RP
http://www.megaupload.com/?d=TOPK8ZFS
http://www.megaupload.com/?d=Q05ZJWG5
http://www.megaupload.com/?d=B8XEWV2Z
http://www.megaupload.com/?d=8MOGLJMP
http://www.megaupload.com/?d=ZWJBPI13
http://www.megaupload.com/?d=8DV6ZVY3
http://www.megaupload.com/?d=6BCYNLJ9
http://www.megaupload.com/?d=2LVRV0BA
http://www.megaupload.com/?d=HBO5XMXK
http://www.megaupload.com/?d=8GBH39SK

http://www.filefactory.com/file/a0f20e8/n/Career_Academy_Certified_Ethical_Hacker_V_6_DVD_3_part1_rar
http://www.filefactory.com/file/a0f20fd/n/Career_Academy_Certified_Ethical_Hacker_V_6_DVD_3_part2_rar
http://www.filefactory.com/file/a0f2h8e/n/Career_Academy_Certified_Ethical_Hacker_V_6_DVD_3_part3_rar
http://www.filefactory.com/file/a0f2b7h/n/Career_Academy_Certified_Ethical_Hacker_V_6_DVD_3_part4_rar

DVD 4
http://www.megaupload.com/?d=Y911ZQU9
http://www.megaupload.com/?d=1CDU8WVH
http://www.megaupload.com/?d=GZJ7R13K
http://www.megaupload.com/?d=1G8QKQLF
http://www.megaupload.com/?d=2ZJGTI1X
http://www.megaupload.com/?d=FAHD4AWY
http://www.megaupload.com/?d=F92GUX8R
http://www.megaupload.com/?d=OA863RV8
http://www.megaupload.com/?d=MB05XE3G
http://www.megaupload.com/?d=57J92C0G
http://www.megaupload.com/?d=PFBK35ZJ
http://www.megaupload.com/?d=02L0N514
http://www.megaupload.com/?d=JOIZNQQ6

MEDIAFIRE

DVD 1
http://www.mediafire.com/?sharekey=86eb05437783626f91b20cc0d07ba4d2ad1aab09128d2ae6
DVD 2
http://www.mediafire.com/?sharekey=86eb05437783626f91b20cc0d07ba4d280a56c67b7af8ade
DVD 3
http://www.mediafire.com/?sharekey=283842fd3dc3e7ef91b20cc0d07ba4d21c75a918e4e1d695
DVD 4
http://www.mediafire.com/?qyxlbbmzzoz
http://www.mediafire.com/?ewptkvwjjsb
http://www.mediafire.com/?wd0pqdhp0dm
http://www.mediafire.com/?yojymmdj9u0
http://www.mediafire.com/?11soyyfi0bg
http://www.mediafire.com/?h0ztj0pm0sb
http://www.mediafire.com/?ybbn3dydlnm
http://www.mediafire.com/?jhkpkd0veiz
http://www.mediafire.com/?et9smil0vod
http://www.mediafire.com/?wdan234s2fy
http://www.mediafire.com/?mzasjj2icyl
http://www.mediafire.com/?g0ndietlmvt
http://www.mediafire.com/?itcexdmjzbx

DVD 5

http://rapidshare.com/files/290451346/Career_Academy_Certified_Ethical_Hacker_V.6_DVD_5.part1.rar
http://rapidshare.com/files/290464777/Career_Academy_Certified_Ethical_Hacker_V.6_DVD_5.part2.rar
http://rapidshare.com/files/290469238/Career_Academy_Certified_Ethical_Hacker_V.6_DVD_5.part3.rar
http://rapidshare.com/files/290480762/Career_Academy_Certified_Ethical_Hacker_V.6_DVD_5.part4.rar
http://rapidshare.com/files/290485652/Career_Academy_Certified_Ethical_Hacker_V.6_DVD_5.part5.rar
http://rapidshare.com/files/290498832/Career_Academy_Certified_Ethical_Hacker_V.6_DVD_5.part6.rar


DVD 6 NEW/NUEVO AND/Y LAST/ULTIMO DVD

http://depositfiles.com/files/68ec00qyb

Si pide Pass es: abu137


LABs DVD-1


http://rapidshare.com/files/290755734/CEHv6-Labs-Volume-1.part01.rar
http://rapidshare.com/files/290755610/CEHv6-Labs-Volume-1.part02.rar
http://rapidshare.com/files/290779521/CEHv6-Labs-Volume-1.part03.rar
http://rapidshare.com/files/290779675/CEHv6-Labs-Volume-1.part04.rar
http://rapidshare.com/files/290803786/CEHv6-Labs-Volume-1.part05.rar
http://rapidshare.com/files/290804651/CEHv6-Labs-Volume-1.part06.rar
http://rapidshare.com/files/290826761/CEHv6-Labs-Volume-1.part07.rar
http://rapidshare.com/files/290827289/CEHv6-Labs-Volume-1.part08.rar
http://rapidshare.com/files/290845845/CEHv6-Labs-Volume-1.part09.rar
http://rapidshare.com/files/290846285/CEHv6-Labs-Volume-1.part10.rar
http://rapidshare.com/files/290863639/CEHv6-Labs-Volume-1.part11.rar
http://rapidshare.com/files/290863790/CEHv6-Labs-Volume-1.part12.rar
http://rapidshare.com/files/290896006/CEHv6-Labs-Volume-1.part13.rar
http://rapidshare.com/files/290895739/CEHv6-Labs-Volume-1.part14.rar
http://rapidshare.com/files/290909872/CEHv6-Labs-Volume-1.part15.rar
http://rapidshare.com/files/290910257/CEHv6-Labs-Volume-1.part16.rar
http://rapidshare.com/files/290923408/CEHv6-Labs-Volume-1.part17.rar
http://rapidshare.com/files/290923473/CEHv6-Labs-Volume-1.part18.rar
http://rapidshare.com/files/290933528/CEHv6-Labs-Volume-1.part19.rar
http://rapidshare.com/files/290933030/CEHv6-Labs-Volume-1.part20.rar
http://rapidshare.com/files/290933664/CEHv6-Labs-Volume-1.part21.rar

http://www.filefactory.com/file/a0gg710/n/CEHv6-Labs-Volume-1_part01_rar
http://www.filefactory.com/file/a0ghbgg/n/CEHv6-Labs-Volume-1_part02_rar
http://www.filefactory.com/file/a0g0h8h/n/CEHv6-Labs-Volume-1_part03_rar
http://www.filefactory.com/file/a0g0hf7/n/CEHv6-Labs-Volume-1_part04_rar
http://www.filefactory.com/file/a0gh083/n/CEHv6-Labs-Volume-1_part05_rar
http://www.filefactory.com/file/a0g0h58/n/CEHv6-Labs-Volume-1_part06_rar
http://www.filefactory.com/file/a0g0h89/n/CEHv6-Labs-Volume-1_part07_rar
http://www.filefactory.com/file/a0f7aa9/n/CEHv6-Labs-Volume-1_part08_rar
http://www.filefactory.com/file/a0f7a4f/n/CEHv6-Labs-Volume-1_part09_rar
http://www.filefactory.com/file/a0f7ag3/n/CEHv6-Labs-Volume-1_part10_rar
http://www.filefactory.com/file/a0f7ce1/n/CEHv6-Labs-Volume-1_part11_rar
http://www.filefactory.com/file/a0f70hf/n/CEHv6-Labs-Volume-1_part12_rar
http://www.filefactory.com/file/a0g0383/n/CEHv6-Labs-Volume-1_part13_rar
http://www.filefactory.com/file/a0f7367/n/CEHv6-Labs-Volume-1_part14_rar
http://www.filefactory.com/file/a0g04cb/n/CEHv6-Labs-Volume-1_part15_rar
http://www.filefactory.com/file/a0f79f1/n/CEHv6-Labs-Volume-1_part16_rar
http://www.filefactory.com/file/a0f8e45/n/CEHv6-Labs-Volume-1_part17_rar
http://www.filefactory.com/file/a0f80hc/n/CEHv6-Labs-Volume-1_part18_rar
http://www.filefactory.com/file/a0f897g/n/CEHv6-Labs-Volume-1_part19_rar
http://www.filefactory.com/file/a0f9gcf/n/CEHv6-Labs-Volume-1_part20_rar
http://www.filefactory.com/file/a0f9hhb/n/CEHv6-Labs-Volume-1_part21_rar

LABs DVD-2

http://rapidshare.com/files/290943538/CEHv6-Labs-Volume-2.part01.rar
http://rapidshare.com/files/290943871/CEHv6-Labs-Volume-2.part02.rar
http://rapidshare.com/files/290954094/CEHv6-Labs-Volume-2.part03.rar
http://rapidshare.com/files/290954124/CEHv6-Labs-Volume-2.part04.rar
http://rapidshare.com/files/290963546/CEHv6-Labs-Volume-2.part05.rar
http://rapidshare.com/files/290963560/CEHv6-Labs-Volume-2.part06.rar
http://rapidshare.com/files/290973187/CEHv6-Labs-Volume-2.part07.rar
http://rapidshare.com/files/290972917/CEHv6-Labs-Volume-2.part08.rar
http://rapidshare.com/files/290982353/CEHv6-Labs-Volume-2.part09.rar
http://rapidshare.com/files/290982508/CEHv6-Labs-Volume-2.part10.rar
http://rapidshare.com/files/290992044/CEHv6-Labs-Volume-2.part11.rar
http://rapidshare.com/files/290992920/CEHv6-Labs-Volume-2.part12.rar
http://rapidshare.com/files/291002697/CEHv6-Labs-Volume-2.part13.rar
http://rapidshare.com/files/291003865/CEHv6-Labs-Volume-2.part14.rar
http://rapidshare.com/files/291015120/CEHv6-Labs-Volume-2.part15.rar
http://rapidshare.com/files/291016593/CEHv6-Labs-Volume-2.part16.rar
http://rapidshare.com/files/291027496/CEHv6-Labs-Volume-2.part17.rar
http://rapidshare.com/files/291029425/CEHv6-Labs-Volume-2.part18.rar
http://rapidshare.com/files/291028252/CEHv6-Labs-Volume-2.part19.rar
http://rapidshare.com/files/291028271/CEHv6-Labs-Volume-2.sfv

http://www.filefactory.com/file/a0f9440/n/CEHv6-Labs-Volume-2_part01_rar
http://www.filefactory.com/file/a0f99a4/n/CEHv6-Labs-Volume-2_part02_rar
http://www.filefactory.com/file/a0gah66/n/CEHv6-Labs-Volume-2_part03_rar
http://www.filefactory.com/file/a0ga757/n/CEHv6-Labs-Volume-2_part04_rar
http://www.filefactory.com/file/a0gbdhe/n/CEHv6-Labs-Volume-2_part05_rar
http://www.filefactory.com/file/a0gb108/n/CEHv6-Labs-Volume-2_part06_rar
http://www.filefactory.com/file/a0gb8g0/n/CEHv6-Labs-Volume-2_part07_rar
http://www.filefactory.com/file/a0gce81/n/CEHv6-Labs-Volume-2_part08_rar
http://www.filefactory.com/file/a0gc38a/n/CEHv6-Labs-Volume-2_part09_rar
http://www.filefactory.com/file/a0gc808/n/CEHv6-Labs-Volume-2_part10_rar
http://www.filefactory.com/file/a0gc9ge/n/CEHv6-Labs-Volume-2_part11_rar
http://www.filefactory.com/file/a0gdb36/n/CEHv6-Labs-Volume-2_part12_rar
http://www.filefactory.com/file/a0gddaf/n/CEHv6-Labs-Volume-2_part13_rar
http://www.filefactory.com/file/a0gde7h/n/CEHv6-Labs-Volume-2_part14_rar
http://www.filefactory.com/file/a0gdf94/n/CEHv6-Labs-Volume-2_part15_rar
http://www.filefactory.com/file/a0gd0hh/n/CEHv6-Labs-Volume-2_part16_rar
http://www.filefactory.com/file/a0gd3f1/n/CEHv6-Labs-Volume-2_part17_rar
http://www.filefactory.com/file/a0gd5d5/n/CEHv6-Labs-Volume-2_part18_rar
http://www.filefactory.com/file/a0gd5e2/n/CEHv6-Labs-Volume-2_part19_rar
http://www.filefactory.com/file/a0gd5e1/n/CEHv6-Labs-Volume-2_sfv

LABs DVD-3


http://rapidshare.com/files/291042892/CEHv6-Labs-Volume-3.part01.rar
http://rapidshare.com/files/291044140/CEHv6-Labs-Volume-3.part02.rar
http://rapidshare.com/files/291056992/CEHv6-Labs-Volume-3.part03.rar
http://rapidshare.com/files/291057666/CEHv6-Labs-Volume-3.part04.rar
http://rapidshare.com/files/291072363/CEHv6-Labs-Volume-3.part05.rar
http://rapidshare.com/files/291073069/CEHv6-Labs-Volume-3.part06.rar
http://rapidshare.com/files/291086715/CEHv6-Labs-Volume-3.part07.rar
http://rapidshare.com/files/291087092/CEHv6-Labs-Volume-3.part08.rar
http://rapidshare.com/files/291100866/CEHv6-Labs-Volume-3.part09.rar
http://rapidshare.com/files/291100942/CEHv6-Labs-Volume-3.part10.rar
http://rapidshare.com/files/291114867/CEHv6-Labs-Volume-3.part11.rar
http://rapidshare.com/files/291114981/CEHv6-Labs-Volume-3.part12.rar
http://rapidshare.com/files/291128914/CEHv6-Labs-Volume-3.part13.rar
http://rapidshare.com/files/291129203/CEHv6-Labs-Volume-3.part14.rar
http://rapidshare.com/files/291141851/CEHv6-Labs-Volume-3.part15.rar
http://rapidshare.com/files/291142169/CEHv6-Labs-Volume-3.part16.rar
http://rapidshare.com/files/291156953/CEHv6-Labs-Volume-3.part17.rar
http://rapidshare.com/files/291157340/CEHv6-Labs-Volume-3.part18.rar
http://rapidshare.com/files/291171719/CEHv6-Labs-Volume-3.part19.rar
http://rapidshare.com/files/291169494/CEHv6-Labs-Volume-3.part20.rar
http://rapidshare.com/files/291169512/CEHv6-Labs-Volume-3.sfv


LABs_ DVD-4


http://rapidshare.com/files/291185072/CEHv6-Labs-Volume-4.part1.rar
http://rapidshare.com/files/291186944/CEHv6-Labs-Volume-4.part2.rar
http://rapidshare.com/files/291200152/CEHv6-Labs-Volume-4.part3.rar
http://rapidshare.com/files/291201890/CEHv6-Labs-Volume-4.part4.rar
http://rapidshare.com/files/291215621/CEHv6-Labs-Volume-4.part5.rar
http://rapidshare.com/files/291217771/CEHv6-Labs-Volume-4.part6.rar
http://rapidshare.com/files/291217989/CEHv6-Labs-Volume-4.part7.rar

read comments Read User's Comments

[Guide] Close any Facebook account in 24 hours.

Close FaceBook account(s)

Just Follow the steps:
Step 1 - Go to this url:
http://www.facebook.com/help/contact.php...m=deceased

So this is the Url we will use to Report our slave. This Form allows you to report a deceased person (someone who is dead).

Step 2 - Complete the Fields:

Explain:
Full Name: Your Victims Full name(Name last name)
Date of birth: Go at his profile and click at Info tab and get his date of birth.
Account Email Addresses: Do the same thing, go to his profile and click on info tab and get his email addresses.
Networks: Again,go to his profile and click on Info tab and get his networks, copy them and paste in the form.
Web address of profile you would like to report: Just go to his profile and copy the link in the address bar.
Relationship to this person: To make more believable select Immediate Family.
Requested Action: Remove Profile
Proof Of Death: This is the hardest part of this form. Now to make a proof of a death just Google in your language a "Death Certificate" or "Certificate of a Death". It doesn't matters from what country you are, just use this Italian certificate and open up photoshop or whatever Image
Editor and just write in a blank field:
Annunciamo il morte di [name goes here]. Save your image to desktop and upload it in one of the Image
Free Hosting like: http://imageshack.us
And it's done ;)... Italian Death Certificate:
Additional Information: Write what you want, just write that you are in his/her family and you would like to close his/her Facebook account because you won't like that when he is dead, his Facebook is opened.

Step 3 - Click on Submit and then a message will appear:
Your injury was submitted at Facebook Team .. So the meaning is that one of the mod's of Facebook will review your report and will do the right decision. It works in most of the times. I closed a few ones.

read comments Read User's Comments

Ultimate Hacking Exposed Ebook Collection Free Download

Hacking Exposed Linux, 3rd Edition

The Latest Linux Security Solutions

This authoritative guide will help you secure your Linux network--whether you use Linux as a desktop OS, for Internet services, for telecommunications, or for wireless services. Completely rewritten the ISECOM way, Hacking Exposed Linux, Third Edition provides the most up-to-date coverage available from a large team of topic-focused experts. The book is based on the latest ISECOM security research and shows you, in full detail, how to lock out intruders and defend your Linux systems against catastrophic attacks.


* Secure Linux by using attacks and countermeasures from the latest OSSTMM research
* Follow attack techniques of PSTN, ISDN, and PSDN over Linux
* Harden VoIP, Bluetooth, RF, RFID, and IR devices on Linux
* Block Linux signal jamming, cloning, and eavesdropping attacks
* Apply Trusted Computing and cryptography tools for your best defense
* Fix vulnerabilities in DNS, SMTP, and Web 2.0 services
* Prevent SPAM, Trojan, phishing, DoS, and DDoS exploits
* Find and repair errors in C code with static analysis and Hoare Logic


Hacking Exposed Computer Forensics, Second Edition: Computer Forensics Secrets & Solutions


The latest strategies for investigating cyber-crime

Identify and investigate computer criminals of all stripes with help from this fully updated. real-world resource. Hacking Exposed Computer Forensics, Second Edition explains how to construct a high-tech forensic lab, collect prosecutable evidence, discover e-mail and system file clues, track wireless activity, and recover obscured documents. Learn how to re-create an attacker's footsteps, communicate with counsel, prepare court-ready reports, and work through legal and organizational challenges. Case studies straight from today's headlines cover IP theft, mortgage fraud, employee misconduct, securities fraud, embezzlement, organized crime, and consumer fraud cases.


* Effectively uncover, capture, and prepare evidence for investigation
* Store and process collected data in a highly secure digital forensic lab
* Restore deleted documents, partitions, user activities, and file systems
* Analyze evidence gathered from Windows, Linux, and Macintosh systems
* Use the latest Web and client-based e-mail tools to extract relevant artifacts
* Overcome the hacker's anti-forensic, encryption, and obscurity techniques
* Unlock clues stored in cell phones, PDAs, and Windows Mobile devices
* Prepare legal documents that will hold up to judicial and defense scrutiny


Hacking Exposed Windows: Microsoft Windows Security Secrets and Solutions


# Establish business relevance and context for security by highlighting real-world risks
# Take a tour of the Windows security architecture from the hacker's perspective, exposing old and new vulnerabilities that can easily be avoided
# Understand how hackers use reconnaissance techniques such as footprinting, scanning, banner grabbing, DNS queries,
and Google searches to locate vulnerable Windows systems
# Learn how information is extracted anonymously from Windows using simple NetBIOS, SMB, MSRPC, SNMP, and Active Directory enumeration techniques
# Prevent the latest remote network exploits such as password grinding via WMI and Terminal Server, passive Kerberos logon sniffing,
rogue server/man-in-the-middle attacks, and cracking vulnerable services
# See up close how professional hackers reverse engineer and develop new Windows exploits
# Identify and eliminate rootkits, malware, and stealth software
# Fortify SQL Server against external and insider attacks
# Harden your clients and users against the latest e-mail phishing, spyware, adware, and Internet Explorer threats
# Deploy and configure the latest Windows security countermeasures, including BitLocker, Integrity Levels, User Account Control,
the updated Windows Firewall, Group Policy, Vista Service Refactoring/Hardening, SafeSEH, GS, DEP, Patchguard, and Address Space Layout Randomization


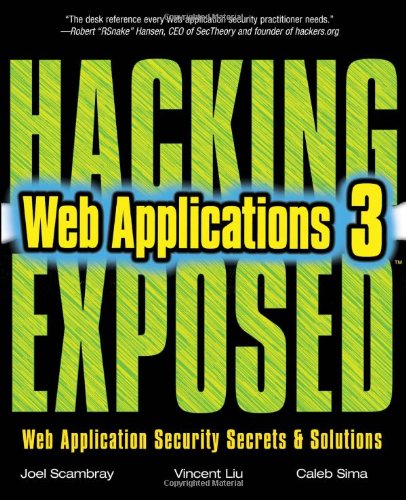
Hacking Exposed: Web Applications, 3rd Edition By Joel Scambray, Vincent Liu, Caleb Sima MG-H, 3rd Edition 2011 | 482 Pages | ISBN: 0071740643 | PDF | 7 MB


The latest Web app attacks and countermeasures from world-renowned practitioners Protect your Web applications from malicious attacks by mastering the weapons and thought processes of today's hacker. Written by recognized security practitioners and thought leaders, Hacking Exposed Web Applications, Third Edition is fully updated to cover new infiltration methods and countermeasures. Find out how to reinforce authentication and authorization, plug holes in Firefox and IE, reinforce against injection attacks, and secure Web 2.0 features. Integrating security into the Web development lifecycle (SDL) and into the broader enterprise information security program is also covered in this comprehensive resource.


* Get full details on the hacker's footprinting, scanning, and profiling tools, including SHODAN, Maltego, and OWASP DirBuster * See new exploits of popular platforms like Sun Java System Web Server and Oracle WebLogic in operation * Understand how attackers defeat commonly used Web authentication technologies * See how real-world session attacks leak sensitive data and how to fortify your applications * Learn the most devastating methods used in today's hacks, including SQL injection, XSS, XSRF, phishing, and XML injection techniques * Find and fix vulnerabilities in ASP.NET, PHP, and J2EE execution environments * Safety deploy XML, social networking, cloud computing, and Web 2.0 services * Defend against RIA, Ajax, UGC, and browser-based, client-side exploits * Implement scalable threat modeling, code review, application scanning, fuzzing, and security testing procedures 


Hacking Exposed: Network Security Secrets and Solutions
Publisher: McGraw-Hill Osborne Media | ISBN: 0071613749 | edition 2009 | PDF | 720 pages | 14,8 mb


Meet the formidable demands of security in today's hyperconnected world with expert guidance from the world-renowned Hacking Exposed team. Following the time-tested "attack-countermeasure" philosophy, this 10th anniversary edition has been fully overhauled to cover the latest insidious weapons in the hacker's extensive arsenal. New and updated material:
- New chapter on hacking hardware, including lock bumping, access card cloning, RFID hacks, USB U3 exploits, and Bluetooth device hijacking
- Updated Windows attacks and countermeasures, including new Vista and Server 2008 vulnerabilities and Metasploit exploits
- The latest UNIX Trojan and rootkit techniques and dangling pointer and input validation exploits...


SIZE 4.9 Mb
Number Of Pages: 400
Publication Date: 2010
ISBN-10 / ASIN: 0071591184
ISBN-13 / EAN: 9780071591188
Publisher:McGraw-Hill Osborne Media 


"A harrowing guide to where the bad guys hide, and how you can find them." --Dan Kaminsky, Director of Penetration Testing, IOActive


"An amazing resource. It is timely, focused, and what we need to better understand and defend against one of the greatest cyber threats we face." --From the Foreword by Lance Spitzner, President of the Honeynet Project


Don't let another machine become a zombie in the malware army


Defend against the ongoing wave of malware and rootkit assaults the failsafe Hacking Exposed way. Real-world case studies and examples reveal how today's hackers use readily available tools to infiltrate and hijack systems. Step-by-step countermeasures provide proven prevention techniques. Find out how to detect and eliminate malicious embedded code, block pop-ups and websites, prevent keylogging, and terminate rootkits. The latest intrusion detection, firewall, honeynet, antivirus, anti-rootkit, and anti-spyware technologies are covered in detail.


• Understand how malware infects, survives, and propagates across an enterprise
• Learn how hackers use archivers, encryptors, and packers to obfuscate code
• Implement effective intrusion detection and prevention procedures
• Defend against keylogging, redirect, click fraud, and identity theft threats
• Detect, kill, and remove virtual, user-mode, and kernel-mode rootkits
• Prevent malicious website, phishing, client-side, and embedded-code exploits
• Protect hosts using the latest antivirus, pop-up blocker, and firewall software
• Identify and terminate malicious processes using HIPS and NIPS 


This book concisely identifies the types of attacks which are faced daily by Web 2.0 sites, and the authors give solid, practical advice on how to identify and mitigate these threats." --Max Kelly, CISSP, CIPP, CFCE, Senior Director of Security, Facebook


• Plug security holes in Web 2.0 implementations the proven Hacking Exposed way
• Learn how hackers target and abuse vulnerable Web 2.0 applications, browsers, plug-ins, online databases, user inputs, and HTML forms
• Prevent Web 2.0-based SQL, XPath, XQuery, LDAP, and command injection attacks
• Circumvent XXE, directory traversal, and buffer overflow exploits
• Learn XSS and Cross-Site Request Forgery methods attackers use to bypass browser security controls
• Fix vulnerabilities in Outlook Express and Acrobat Reader add-ons
• Use input validators and XML classes to reinforce ASP and .NET security
• Eliminate unintentional exposures in ASP.NET AJAX (Atlas), Direct Web Remoting, Sajax, and GWT Web applications
• Mitigate ActiveX security exposures using SiteLock, code signing, and secure controls
• Find and fix Adobe Flash vulnerabilities and DNS rebinding attacks

read comments Read User's Comments